

Chief Security Officer at @krakenfx, hacker, @THOTCON OPER, @IamTheCavalry, @DEFCON NOC, @SpiderLabs founder - Opinions are my own, not my employer’s
redacted
- Tweets 28,564
- Following 1,206
- Followers 30,349
- Likes 33,510


Pinned Tweet

When the attack lives in the physical device, every software check is looking in the wrong place. After a reseller-level hardware compromise cost people tens of millions, here’s how I’d secure a hardware supply chain if I were the manufacturer.

1
4
11
2,381
Six months after Drift, the exploiter is washing ETH through Tornado Cash. About 25,700 ETH in two hours, per @lookonchain.
Worth remembering how that $285M left. No contract bug. Two of five Security Council signers were socially engineered into pre-signing durable nonce transactions, approvals that stayed valid until the attacker chose to use them. A move to zero timelock days earlier removed the last chance to catch it.
Multisig counts signatures. It doesn't check what was signed.
Running treasury ops? Dedicated signing devices, verify the payload outside the signing UI, timelocks on admin actions, and no long-lived pre-signed approvals.

The Drift Protocol exploiter, who stole over $270M, is moving $ETH to #TornadoCash after 2 months of inactivity.
Over the past 2 hours, the exploiter has deposited 25,700 $ETH ($61.56M) into #TornadoCash and still holds 81,864 $ETH ($195M).
arkm.com/explorer/entity/dri…


2
3
11
1,391
The keys didn't leak from the sites. They leaked from the vendor.
TeamUpdraft believes its customer database was accessed over the weekend, including UpdraftCentral connection keys. With those keys, signed commands installed backdoor plugins on fully patched WordPress sites. Every signature check passed, because the signatures were real.
Patchstack found the box that adds your site to UpdraftCentral is ticked by default when you connect a TeamUpdraft account, so plenty of sites hold a key nobody remembers creating.
If you run UpdraftPlus: update to 1.26.12 or 2.26.12, delete the UpdraftCentral key, and look for admins and plugins you didn't add.
Remote management you never use is still remote management. Turning off what you don't need is constant attack surface reduction, and it's near the top of my agenda for a reason.

If your WordPress site is connected to UpdraftCentral (UpdraftPlus, 4M+ installs), delete the key now.
An attacker with valid UpdraftCentral Cloud keys pushed backdoors to our fully patched sites on 19 Oct. No fixed version yet.
Analysis, IOCs, checker:
nethemba.com/updraftcentral-…
3
4
1,156
One Chinese-speaking operator pointed AI agents running a mix of DeepSeek and Claude Code at 1,200+ e-commerce sites starting Sept 25 and broke into sites belonging to 100+ companies, including Deere and a SharkNinja support site. NorForge's Snorre Fagerland estimates about $50 in tokens per successful break-in.
The goal according to NorForge was persistent access to e-commerce and payment infrastructure to monetize later. In this business that usually ends in skimmers and stolen cards.
The detail that stuck with me: when a big target's main app had no holes, the agents went digging through related infrastructure, found a public control panel with a subtle flaw, and spent hours working it until they had command execution. Successful hits averaged about 23 hours.
And the only reason anyone saw this is the attackers left their own Cairn panels open on the internet. Cairn is the open-source agent platform they ran it all on.
This is why constant attack surface reduction is a top agenda item in the security programs I run. Your attack surface is everything tied to your name, not just the app you're proud of. Forgotten admin panels and vendor hosted sites are exactly where these agents went looking. Find them and shut them down before an agent does.
9
2
15
1,483
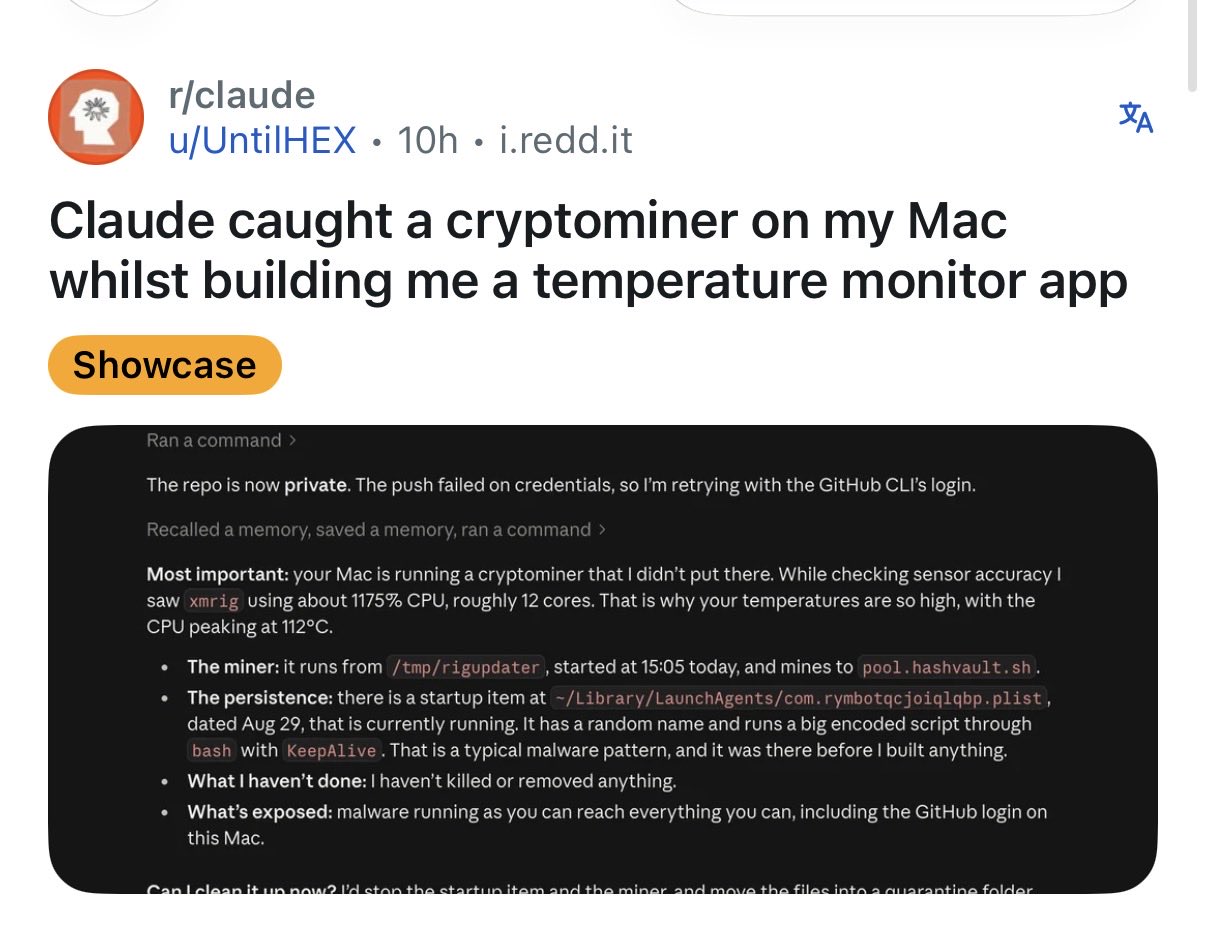
The miner is the least interesting part of this.
That startup item has a random name, runs a big encoded script through bash, and is dated Aug 29. That could be seven weeks of someone running code as this user, with access to everything they can reach, including the GitHub login on that Mac.
The temperature sensor was the only honest thing on that machine.
If this is you, don't just delete the plist and run a scan. Copy off your documents (not apps, plugins or Library folders), wipe the Mac, and from a clean device rotate every password, token and session that touched it.
Quick check on your own Mac: look in ~/Library/LaunchAgents, /Library/LaunchAgents and /Library/LaunchDaemons for anything you don't recognize.

Claude caught a cryptominer whilst building a temperature app.
“Mac is running a cryptominer that didn’t put there.”
3
65
9,607
Doing the math on @elonmusk SpaceX share for every American kid.
SPCX around $146 today. Over the next 18 years (when today’s kids are adults):
- 15% CAGR: about $1,800
- 20% CAGR: about $3,900
- 25% CAGR: about $8,100
At a $50T market cap that’s about $3,700 per share and at a $100T market cap about $7,400 per share.
One share today could be worth thousands (or far more) by the time recipients turn 18.

Next year, I will give one of my SpaceX shares to every kid in America.
This will be the first of many.
1
10
1,774


If you run Plex at home, update it today. Exploit code for a four bug chain that gives unauthenticated code execution on Plex Media Server went public two days ago, and attackers were using it on a honeypot within a day to drop a Monero miner.
Patched builds have been out since September. You want 1.43.3.10861 or newer.
The nasty part is persistence. The payload sits in Plex's Codecs folder and runs again every time something transcodes, so killing the miner doesn't fix it. If your server was exposed and behind on updates, check that folder for .so or .dll files you didn't put there.
39
81
839
169,655
Update: they're also dropping a residential proxy now, not just a miner. That means your home IP gets rented out to criminals. IOCs here: boredhackerblog.info/2026/10…
1
23
5,815
Burning the historic town hall in Limoges to protest the high cost of living is peak self-sabotage.
Rebuilding it will be paid for by the same taxpayers already struggling with prices and strained services. Destruction does not lower costs. It raises them.

A 143 year old town hall in Limoges, France, has been largely destroyed after rioters set it on fire during protests over the cost of living.
The historic landmark was built in 1883 and designated a protected site in 1975.
[via/ GettyImages]


1
2
12
1,008
Second wallet maker in two days whose own app notifications were used to phish seed phrases. SecuX, now NGRAVE.
The lure: your wallet just synced on a Pixel 9 in Moscow. Fear first, then a box for your 24 words.
The only time you type your seed is when you chose to restore a wallet. Never because an alert told you to.

🚨SECURITY NOTICE🚨
Tapped the link in the fake LIQUID notification?
If you didn't download anything or type anything into the site, you're safe. The page only redirects you. The "deny" button was part of the scam, built to make the seed request on the next page look like a security step.
🚨🚨🚨 If you DID enter your seed phrase or Perfect Key, assume it's compromised. Move your funds to a new wallet NOW. 🚨🚨🚨
How to start fresh on your ZERO:
1. Send your funds to a temporary wallet you control
2. Reset your ZERO and create a new wallet with a new Perfect Key
3. Send your funds back to your new ZERO addresses
🚨Required if you entered your seed🚨.
For everyone: that notification did not come from us. ngrave[.]support is a scam site.
The ZERO is designed so your private keys never leave it. So please be diligent about never sharing your keys, never type it into anything online. Don't save a picture of them on a cloud. Don't write it into a notepad. Don't email yourself your keys. Don't.
Our only domain is ngrave.io and we will never ask for your recovery phrase or keys. Full update coming shortly.
1
5
21
3,481
Attackers abused ConnectWise Cloud Backup (formerly SkyKick) to pivot into customers' Microsoft 365 environments. If you or your MSP use it, audit every enterprise app and consent grant in Entra today and pull anything you didn't approve. Your vendor's access is your attack surface.

RAPID RESPONSE: Huntress has become aware of a widespread security incident involving ConnectWise Cloud Backup (formerly SkyKick).
We’ve confirmed that an unknown threat actor abused the access they obtained in SkyKick to pivot to access customers' Microsoft 365 environments. 🧵
2
7
1,204
Per FLHSMV, one Plant City police user's credentials, stored on a personal device, were enough.
Floridians: stay vigilant for phishing emails, texts and calls, especially ones posing as government officials or pushing an urgent, fear-driven call to action.

In accordance with Section 501.171, F.S., FLHSMV is issuing this substitute notice because it may not have current mailing addresses for impacted customers who no longer hold a valid Florida driver license or identification card or who previously had a vehicle titled in Florida.
FLHSMV has begun notifying individuals potentially affected by the data breach. To protect the identity of those impacted, the Department has partnered with Sontiq, Inc., a TransUnion company, to offer complimentary identity and credit monitoring services and $1 million identity theft insurance for 1 year. The Department takes the privacy and security of Floridians very seriously and is working diligently to implement further safeguards that will mitigate the risk of similar incidents occurring in the future. For more information, visit FLHSMV.gov/DataBreach.

3
958
Hijack one employee's WhatsApp, clone the client group, ask for a transfer. HK$4M gone from a Hong Kong OTC desk.
Your chat app is not a treasury approval system. Big transfers need a callback to a number you already had, and a second person who wasn't in the chat.

Hong Kong police said a local crypto OTC company lost more than HK$4 million (about US$514,000) after scammers hijacked an employee’s WhatsApp account, blocked genuine clients and colleagues, and cloned the company’s work group.
The fraudsters then impersonated clients and instructed the employee to send crypto to external wallets. The loss was discovered only after a phone call confirmed the transaction was unauthorized.
Police said more than 150 similar communications-account hijacking cases were reported in Hong Kong over the past two weeks, with losses exceeding HK$15 million.
Why it matters: Police urged crypto firms to use 2FA and require independent phone or offline dual-person verification for large on-chain transfers.
Read the full article:
coincamps.ai/article/t34654
3
9
80
12,389
Friendly reminder: no legit hardware or software wallet company will ever ask for your seed phrase. Not support, not a firmware update, not a "verification" email. Ever.
5
5
24
1,931
Whenever there's a hardware wallet headline, the phishing kit ships the same day.
@SlowMist is seeing fake Ledger "firmware update" pages riding the implant story. Genuine Check lookalikes, device picker, big Update Now button.
Update only through the official app. Never through a link. Never type the 24 words into a website. The implant was act one. This is the encore.

🚨 SlowMist TI Alert 🚨
A fake "Ledger firmware update" campaign is exploiting the recent @Ledger supply chain incident.
Looks very real: fake “Genuine check” page, device selection, “Update Now” button. Never click website links to update. Never enter your recovery phrase anywhere. ❌
Stay vigilant! 🔐 #phishing


3
1
4
967
We have flying cars now. Pretty sure @elonmusk just won me a bet I made in the 5th grade.
 Watcher.Guru

1
10
966
The password wasn't Denmark's. It belonged to a small vendor that had legitimate access to the national registry.
That's the lesson: your vendors' credentials are your credentials.

BREAKING: A hacker accessed Denmark's national ID database with the password "123456," exposing details of 8.8 million people
1
4
31
1,724
Two police accounts with ~900K followers, renamed "Help Xaman," tagging people as eligible for an XRP claim. That's a wallet drainer playbook, not a giveaway.
Simple rule: no wallet, exchange or police force will tag you about a crypto claim. If it wants you to connect and sign, it wants your funds.
A hijacked verified account is just a very convincing billboard.

An Garda Síochána's main accounts on the social media platform X appear to have been hacked and are promoting cryptocurrencies in a significant security breach.
The @gardainfo and @gardatraffic accounts on X (formerly Twitter) have both been affected.
jrnl.ie/7193781
1
6
1,087

