Follow @ma1 for latest news about NoScript and web browser security. Use NoScript to protect yourself against malicious web content. noscript.net/donate

YES
Countless worse ways to invest your money... DONATE NOW! 💜🧅
1
17
NoScript 🐘 noscript@mastodon.social retweeted
.@OpenTechFund's Security Lab partner @SecReLabs recently audited @noscript to ensure it offers users the best possible security. Learn more: ow.ly/Qz5Z50ZSraJ
2
4
409
NoScript 🐘 noscript@mastodon.social retweeted
The top @noscript banner looks like a solid start.
Je lance l’initiative Exit Chat Control. exitchatcontrol.org/ Ce site est un guide complet qui vise à répertorier tous les outils nécessaires pour contourner tout système de surveillance de vos messageries privées. Le site est open source et sera amélioré en continu.
1
2
203
NoScript 🐘 noscript@mastodon.social retweeted
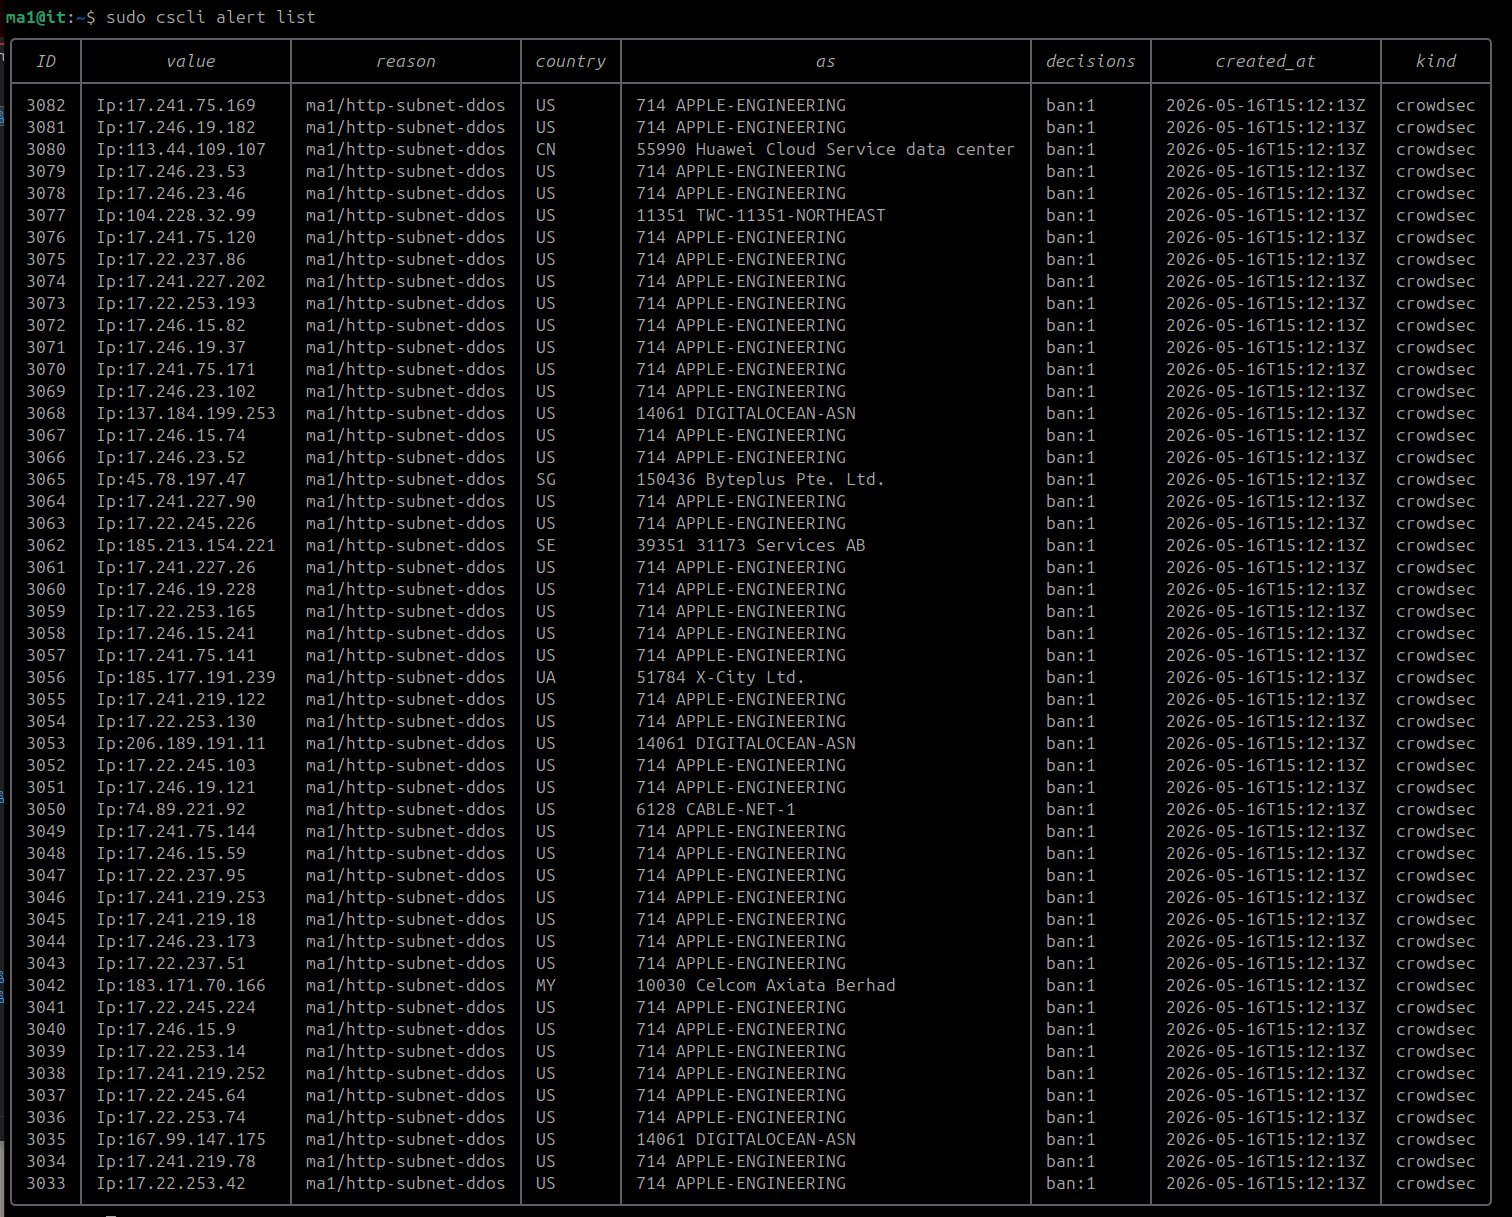
I thought it was the usual DDOS spidering fuckery by Bytedance (TikTok) putting @noscript's support forums on their knees, but... APPLE ENGINEERING, WTF?!!! "Ambassador" Tim Cook, his new CEO & their minions embracing the dark side really hard 🪱🍏
2
2
286
NoScript 🐘 noscript@mastodon.social retweeted
And that's why the dependencies of @noscript + NoScript Commons Library amount to a grand total of 5 self contained, vendored source files.
There is a project on GitHub called Axios. Axios is extremely popular. It is used by millions upon millions of applications. Axios is a programming library that helps your JavaScript code make HTTP/S requests (communicate with websites). In simple terms, if you're a programmer doing something with JavaScript, and want to do stuff that communicates with a website in literally any capacity, people heavily recommend using Axios due to its simplicity. Using Axios you don't have to reinvent the wheel and do a bunch of work. All you need to do is import Axios into your code and you're off to the races. Someone (currently unknown) compromised Axios (currently unknown how) to deliver malware to people. When someone updates or installs Axios, Axios itself contains malware. What the malware does is (currently) unknown, but it is being reversed engineered by probably every malware analyst on the planet at this moment. In a few hours more details will emerge. Information is being exchanged in real time on social media and private communication platforms as I write this. Due to the size and popularity of Axios, it is unknown how many are impacted, it could be millions, it could be thousands, or if we're lucky, only hundreds of people or organizations will be impacted. If this is absolute worst case scenario, millions of organizations across the planet have been infected with malware which (currently) we do not understand. However, the likelihood of this is low. It appears Axios being compromised was detected quickly, potentially within minutes (or hours) of it being compromised to deliver malware. Additionally, the likelihood of every single Axios user updating Axios as soon as it was compromised to deliver malware is astronomically low. It is basically zero. The impact from Axios being compromised is devastating, the fallout from this will be a massive headache. This is unironically a malware nuclear missile and will likely be studied in the future.
3
5
370
13.6.6 just out: - "S" gesture optional & disabled by default - Enable it in Options>Appearance to skip the new Android Firefox menu 3 taps navigation - Lowered activation threshold + tooltip to guide the gesture Thanks for your patience, and your past & future feedback❤️
2
2
5
223
New "S" gesture for Android in NoScript 13.6.x, along with other less visible improvements in policy enforcement, both in NoScript proper and in the NoScript Commons Library. noscript.net/getit
New @firefox for Android menu buries extensions deep down into a click pit. But now you can summon your @noscript quicly by sketching a "S" on the web page😎
1
2
224
Casual reminder about NoScript's mitigations going far beyond selective #JavaScript execution (on @firefox-based browser at least, such as @torproject & @mullvadnet). #ConsensualBrowsing
It couldn't work in the Tor Browser, neither in the @mullvadnet Browser, because of @noscript's noscript.net/usage/#lan-prot… (independent from #JavaScript blocking, which may help as well).
1
1
3
145
NoScript 🐘 noscript@mastodon.social retweeted
The quick @firefox jumps over the lazy laptop.
1
2
121
📯NoScript 13.5.6 is out! Main news: - New option to disable automatic page reloading on permissions change - Fix quirks mode rendering bug on cold load of pages from file:// URLs ⬇️ noscript.net/getit
3
5
143
#NoScript 13.5 is out, with many user experience improvements: - cascade permissions" mode - onboarding / site classification behavior panel - many content #usability and #security enhancements Special thanks to @OpenTechFund for their strenuous support! noscript.net/
1
5
363
"We decided to move control of Wasm to @noscript, which bundled with Tor Browser & already manages #JavaScript & other security features. Wasm now works on privileged browser pages such as the PDF renderer, but NoScript will continue blocking the technology on regular websites"
🎉 Tor Browser 15.0 is now available! Our first stable release based on Firefox ESR 140, incorporating a year's worth of changes. Download now from the Tor Browser download page: blog.torproject.org/new-rele…
2
3
224
NoScript 🐘 noscript@mastodon.social retweeted
Both disturbing and bizarre. Why is an administration that says it supports open-weight models and real competition in AI deleting government materials that support its position?
New, from me and @kellymakena: The FTC is disappearing blog posts about AI that were written during Lina Khan’s tenure as FTC chair wired.com/story/ftc-removes-…
21
277
1,661
99,752
NoScript 13.2.2 is out: - Works around a a long-standing breakage on Proton Mail - Erases temporary permissions when last tab is closed on Android, as a work-around for the "Quit" browser menu command actually keeping Firefox alive, even if hidden. noscript.net/getit
2
3
161
NoScript 🐘 noscript@mastodon.social retweeted
🚨 Double your impact 🚨 Although the modern internet has been corrupted by rampant privacy violations and pervasive government spying, we have the power to FREE THE INTERNET from the chains of censorship and surveillance. ⛓️‍💥 Donate today to take advantage of our match offered by Power Up Privacy and support a free internet. This means a $25 donation will have a $50 impact. torproject.org/donate/donate…
6
21
95
8,599
"Your WAF can't see this." My users can (hope they're your customers)😄
Your WAF can’t see this. Attackers are skimming payment data right now through unmonitored JavaScript—while your dashboards stay clean. The worst part? It’s happening in your customers’ browsers. See what every retailer must fix before Black Friday ↓ thehackernews.com/2025/10/wh…
1
1
111
NoScript 13.1 is out. - New wasm capability for per-site WebAssembly control - Fix for some visual breakages where unrestricted CSS is off - Best effort avoidance of extra tab bars for AI Chatbot sidebar detection noscript.net/getit
1
3
7
446
NoScript 🐘 noscript@mastodon.social retweeted
Based on reports up to September 2025: Chrome: 6 zero-days exploited (e.g., CVE-2025-10585, per The Hacker News, SocPrime, and Google updates). Firefox: 3 zero-days exploited (CVE-2025-2857, CVE-2025-4918, CVE-2025-4919, per Bleeping Computer, The Hacker News, and Mozilla advisories). NoScript can help mitigate unknown vulnerabilities by blocking JavaScript execution, a common exploit vector (per NoScript docs and security analyses).
2
4
263
NoScript 🐘 noscript@mastodon.social retweeted
🔥#chrome #0day actively exploited in the wild. 🦊 Switch to @firefox 🚫 use @noscript 📲 On Android, too #zerodayattack #zerodayexploit #security
🚨 CISA Warns of Google Chrome 0-Day Vulnerability Exploited in Attacks Read more: cybersecuritynews.com/cisa-g… CISA has issued a warning about a high-severity zero-day vulnerability in Google Chrome that is being actively exploited in attacks. The vulnerability, tracked as CVE-2025-10585, has been added to CISA’s Known Exploited Vulnerabilities (KEV) catalog, signaling an urgent need for users and administrators to take action. #cybersecuritynews #Vulnerability
1
2
404