
Custom x64 API resolver designed for Win64 shellcodes & loaders. 100% assembly-native recursive forwarding (no CRT, no C helpers). Source code polymorphism to blend gs:[0x60] PEB reads. Adheres to Windows x64 ABI.
github.com/Proteqtum/Win64-A…
#MalwareDev #RedTeam #BlueTeam #WindowsInternals
1
71

Released my EDR evasion loader research from the DEF CON 34 workshop.
Fun project!
Chains PEB walking -> API hashing -> module stomping -> fiber execution
codeberg.org/MyuraASM/edr-ev…
#malwaredev #EDR #infosec #DEFCON #redteam

5
2
282

project to dynamically allocate and specify the address of g_CiEnabled kernel variable responsible for enabling and disabling DSE in Windows Systems
github.com/ring0shady/g_CiEn…
#MalwareDev #RedTeam #OffensiveSecurity #ReverseEngineering #ExploitDev #PenTest #KernelHacking #Ring0

8
714

TYPES OF CRYPTO SCAMS ⚫️
#MalwareDev #phishing #ico #website #Cloning #PumpDumps #ponzi #fake #wallet fake support team #EpsteinFiles #Crypto

12
1
20
301

Big drop: ClickFix campaign hits legit sites like bincheck.io & investonline.in. Fake jQuery inject → bogus Cloudflare page → tricks users to copy/run PowerShell from clipboard. Stealthy bypass of browser protections.
#Malware #MalwareDev #Exploit #RAT


1
4
184

Check out the new post about XWorm written by my friend @0x_Olympus!
#cybersecurity #MalwareDev #bolhasec

🚨 LATAM businesses are being hit by #XWorm via fake financial receipts.
SOCs report stolen creds, account takeovers, follow-on incidents ⚠️
Read the full breakdown from @0x_Olympus and learn how to cut risk with earlier monitoring and faster triage 👇
any.run/cybersecurity-blog/x…
1
3
278

Fun experiment while preparing for a presentation: Asked #AI to create a privilege escalation demo binary for Windows.
Got a complete, working tool with token duplication → SYSTEM elevation in <15 minutes. AI even generated its own prompt 😍. #MalwareDev


8
315

Sophisticated Malware Campaign Uses Fileless Techniques to Deploy Remcos RAT
Windows malware is evolving and this campaign proves it. What looks like a simple click can now unlock full remote control.
#windows #MalwareDev #CybersecurityNews
Full Story 👉
cybersecurity88.com/news/new…

2
96

In the wild, a raw payload gets caught.
To survive the EDR, you have to blend in.
To break the system, you must become the system. 🦎
#MalwareDev #OpSec #DarkVeinC2 #OffensiveSecurity #Comics

1
1
152
Security Teams Spot Experimental Shai-Hulud Malware with Advanced Obfuscation
🧬 A familiar malware name is quietly evolving. And it’s happening inside the software supply chain.
#MalwareDev #cybersecuritynews
Full Story 👉
cybersecurity88.com/news/new…

2
149


Started a collection of Rust code samples useful for malware development!
Gonna be ongoing additions to the repo as I learn more Rust dev.
Repo: github.com/wsummerhill/Rusty…
#rust #malwaredev #redteam

3
124

Te permite ver:
✔ flujo real
✔ trampas de ofuscación
✔ lógica oculta
✔ syscalls sospechosas
#Reverse #Syscalls #MalwareDev #CyberSkills
1
3
257

❗️Blog Alert
💥Crafting maskable functions using LLVM.
🔎In depth coverage of LLVM backend internals.
🔎Tinker with x64 function code stubs and manipulate control flow
This time, I am posting it on @MDSecLabs blog😋
#RedTeaming #MalwareDev
mdsec.co.uk/2025/10/function…
1
4
19
1,706

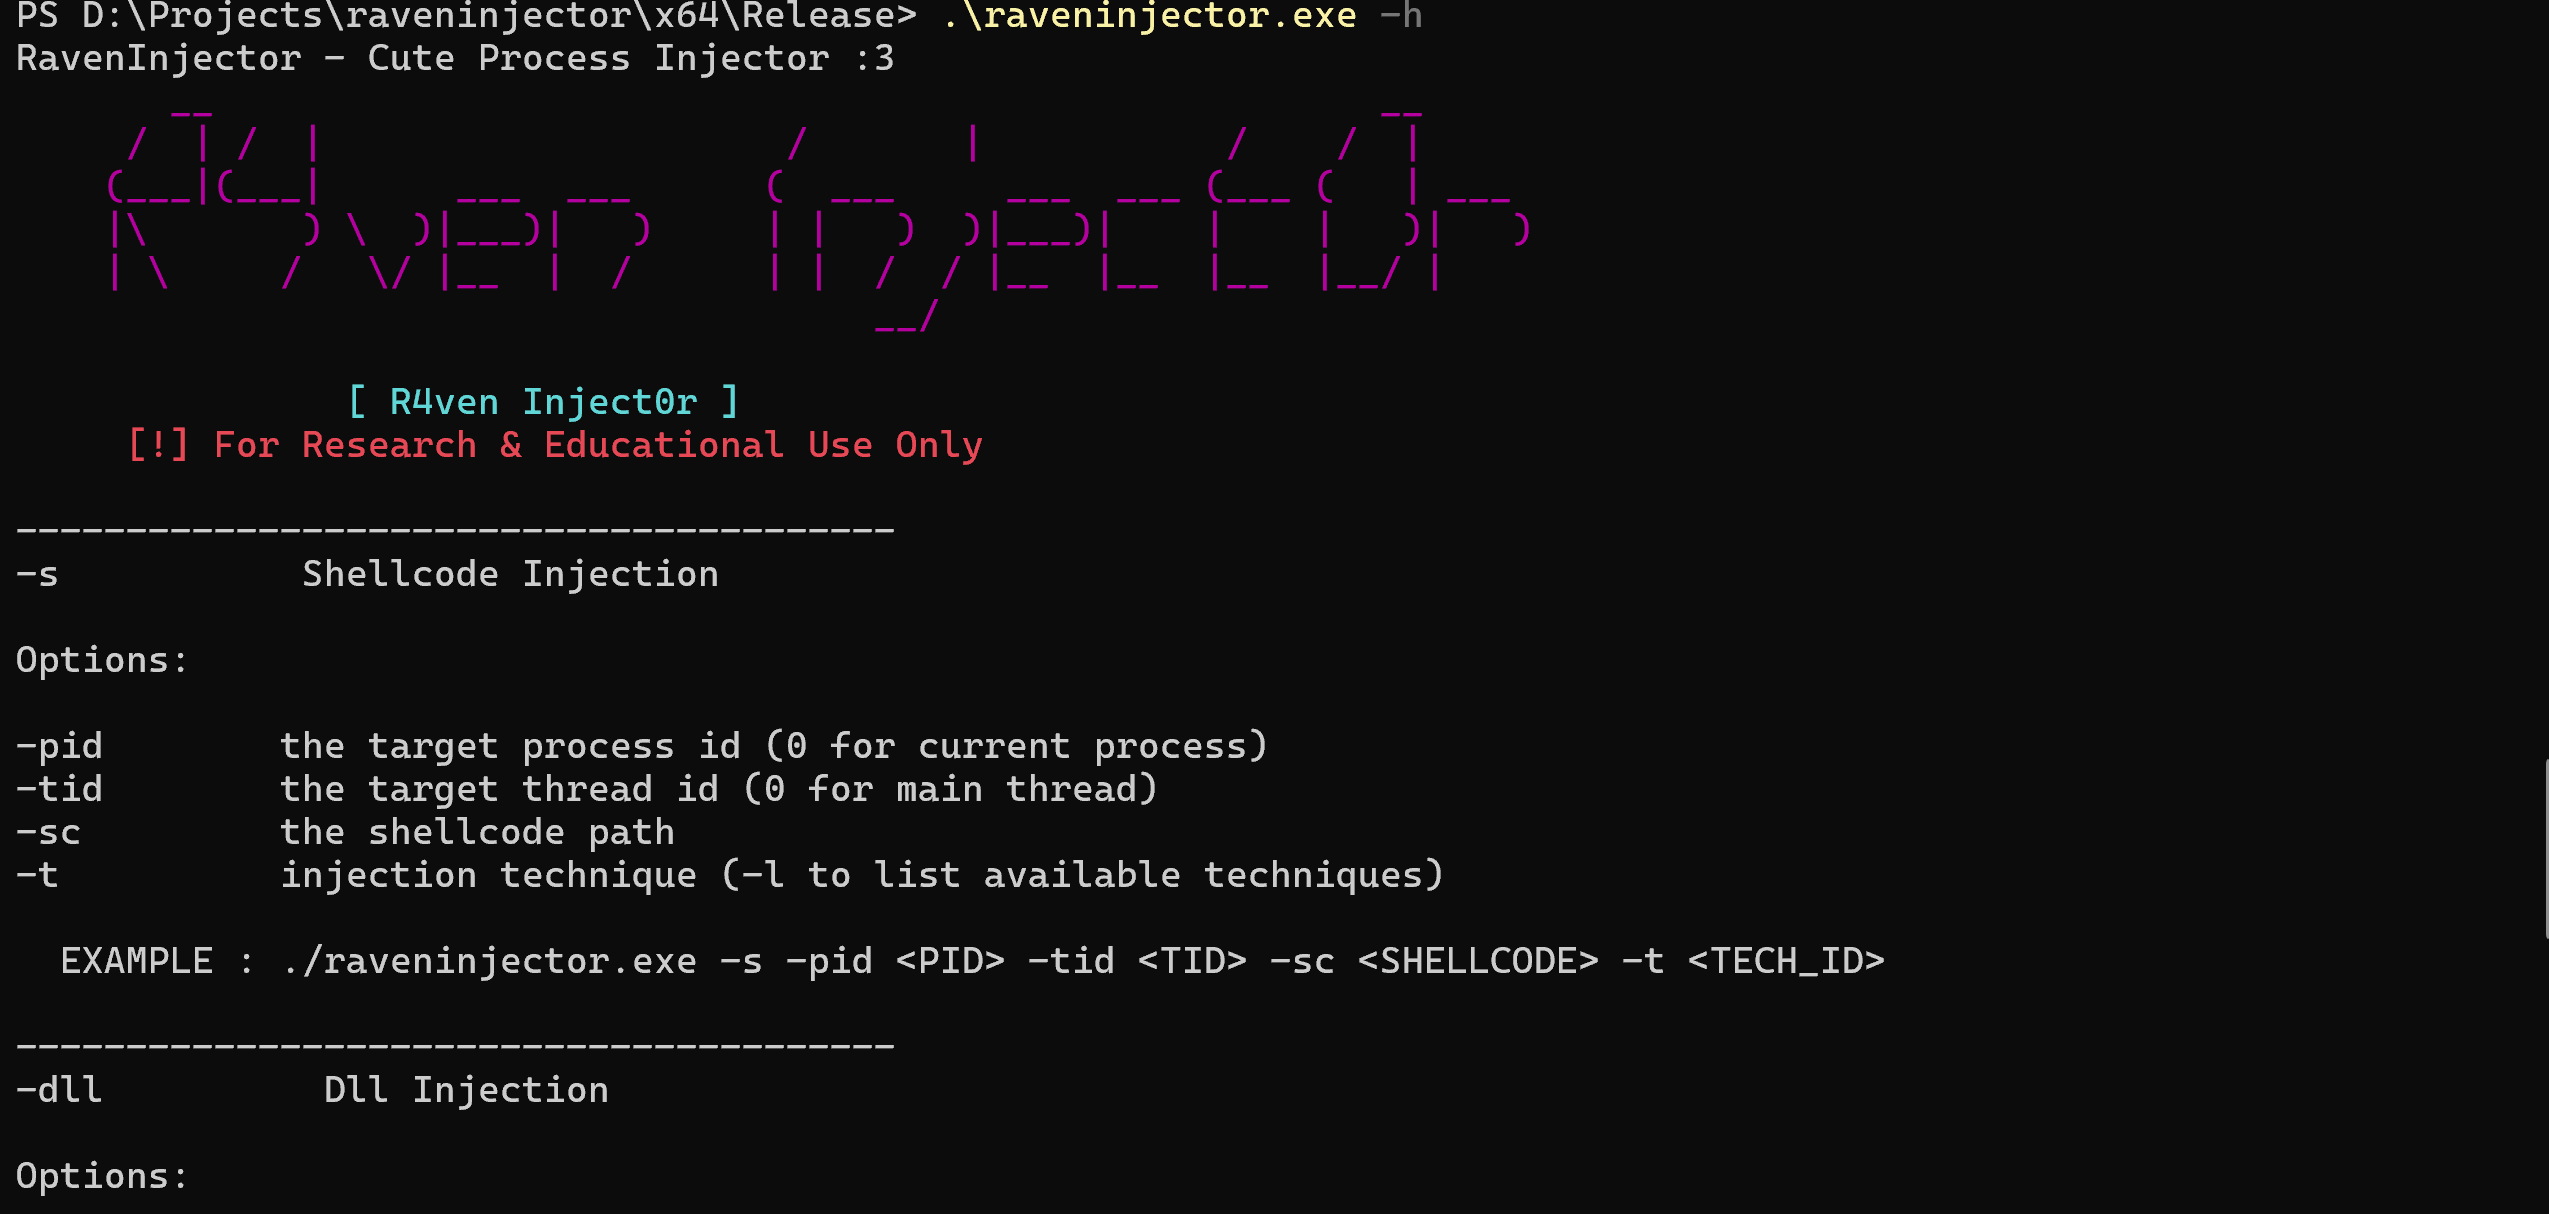
github.com/B4shCr00k/R4venIn…
Just Another Process Injector :3
- x64 only
- Dll / Shellcode Injection
- Many techniques
#malware #exploits #malwaredev #tools #github #Windows11
2
191

Think your tools are stealthy? Think again. This course teaches how to break detection, unhook APIs, bypass ETW/AMSI, and weaponize obfuscation like top-tier APTs. If you're not evading, you're just noisy. Meet us at @BlackHatEvents! #RedTeam #MalwareDev #CyberSecurity #BHUSA #Obfuscation
2
9
725

Everyone says ‘just modify the PE headers’ like it’s easy. Bro, I barely understand what the headers even do. One wrong edit and my file just refuses to run.😭 #MalwareDev
2
6
203

Tool Update: LitterBox v1.5
What's New:
- New scanner RedEdr added to the arsenal.
- Refactored some server-side code for better performance.
- Major UX/UI improvements for smoother navigation.
#MalwareDev #sandbox #RedTeam

Tired of switching tools for payload testing? LitterBox - bringing Moneta, PE-sieve & more into one unified platform.
github.com/BlackSnufkin/Litt…
#RedTeam #MalwareDev #CRTL
1
1
9
583
Tired of switching tools for payload testing? LitterBox - bringing Moneta, PE-sieve & more into one unified platform.
github.com/BlackSnufkin/Litt…
#RedTeam #MalwareDev #CRTL
2
38
137
11,055

cocomelonc.github.io/malware… next one on my blog. This post is the result of my own research on implementing Walsh Transform. #malware #malwaredev #malwareanalysis #cybersecurity #hacking #redteam #blueteam #purpleteam #cryptography #math #research #programming #cryptanalysis
8
40
1,609